Implement PCI DSS compliance requirements for secure
Pci compliance
Implement PCI DSS compliance requirements for secure handling of payment card data and payment systems. Use when securing payment processing, achieving PCI compliance, or implementing payment card security measures.
---
name: pci-compliance
description: Implement PCI DSS compliance requirements for secure handling of payment card data and payment systems. Use when securing payment processing, achieving PCI compliance, or implementing payment card security measures.
---

# PCI Compliance

Master PCI DSS (Payment Card Industry Data Security Standard) compliance for secure payment processing and handling of cardholder data.

## When to Use This Skill

- Building payment processing systems
- Handling credit card information
- Implementing secure payment flows
- Conducting PCI compliance audits
- Reducing PCI compliance scope
- Implementing tokenization and encryption
- Preparing for PCI DSS assessments
Overview
Master PCI DSS (Payment Card Industry Data Security Standard) compliance for secure payment processing and handling of cardholder data.
Manual install (npx, ZIP)
npx skills add wshobson/agents --skill pci-compliance -g -a claude-codemkdir -p ~/.claude/skills && curl -sL https://codeload.github.com/wshobson/agents/tar.gz/4236bb91f839 \
| tar -xz -C ~/.claude/skills --strip-components=4 agents-4236bb91f839/plugins/payment-processing/skills/pci-complianceNew-Item -ItemType Directory -Force "$HOME\.claude\skills" | Out-Null; Invoke-WebRequest "https://m.agentalley.io/zip/2093ca939f5de07742ac/pci-compliance.zip" -OutFile "$env:TEMP\pci-compliance.zip"; Expand-Archive "$env:TEMP\pci-compliance.zip" -DestinationPath "$HOME\.claude\skills" -ForceConnects with Agent Alley MCP · agentalley.io/mcp
Files included
SKILL.md7.5 KBreferences/1 file · 4.5 KB
Read the files here
Show the full text274 lines
PCI Compliance
Master PCI DSS (Payment Card Industry Data Security Standard) compliance for secure payment processing and handling of cardholder data.
When to Use This Skill
- Building payment processing systems
- Handling credit card information
- Implementing secure payment flows
- Conducting PCI compliance audits
- Reducing PCI compliance scope
- Implementing tokenization and encryption
- Preparing for PCI DSS assessments
PCI DSS Requirements (12 Core Requirements)
Build and Maintain Secure Network
- Install and maintain firewall configuration
- Don't use vendor-supplied defaults for passwords
Protect Cardholder Data
- Protect stored cardholder data
- Encrypt transmission of cardholder data across public networks
Maintain Vulnerability Management
- Protect systems against malware
- Develop and maintain secure systems and applications
Implement Strong Access Control
- Restrict access to cardholder data by business need-to-know
- Identify and authenticate access to system components
- Restrict physical access to cardholder data
Monitor and Test Networks
- Track and monitor all access to network resources and cardholder data
- Regularly test security systems and processes
Maintain Information Security Policy
- Maintain a policy that addresses information security
Compliance Levels
Level 1: > 6 million transactions/year (annual ROC required) Level 2: 1-6 million transactions/year (annual SAQ) Level 3: 20,000-1 million e-commerce transactions/year Level 4: < 20,000 e-commerce or < 1 million total transactions
Data Minimization (Never Store)
# NEVER STORE THESE
PROHIBITED_DATA = {
    'full_track_data': 'Magnetic stripe data',
    'cvv': 'Card verification code/value',
    'pin': 'PIN or PIN block'
}

# CAN STORE (if encrypted)
ALLOWED_DATA = {
    'pan': 'Primary Account Number (card number)',
    'cardholder_name': 'Name on card',
    'expiration_date': 'Card expiration',
    'service_code': 'Service code'
}

class PaymentData:
    """Safe payment data handling."""

    def __init__(self):
        self.prohibited_fields = ['cvv', 'cvv2', 'cvc', 'pin']

    def sanitize_log(self, data):
        """Remove sensitive data from logs."""
        sanitized = data.copy()

        # Mask PAN
        if 'card_number' in sanitized:
            card = sanitized['card_number']
            sanitized['card_number'] = f"{card[:6]}{'*' * (len(card) - 10)}{card[-4:]}"

        # Remove prohibited data
        for field in self.prohibited_fields:
            sanitized.pop(field, None)

        return sanitized

    def validate_no_prohibited_storage(self, data):
        """Ensure no prohibited data is being stored."""
        for field in self.prohibited_fields:
            if field in data:
                raise SecurityError(f"Attempting to store prohibited field: {field}")
Tokenization
Using Payment Processor Tokens
import stripe

class TokenizedPayment:
    """Handle payments using tokens (no card data on server)."""

    @staticmethod
    def create_payment_method_token(card_details):
        """Create token from card details (client-side only)."""
        # THIS SHOULD ONLY BE DONE CLIENT-SIDE WITH STRIPE.JS
        # NEVER send card details to your server

        """
        // Frontend JavaScript
        const stripe = Stripe('pk_...');

        const {token, error} = await stripe.createToken({
            card: {
                number: '4242424242424242',
                exp_month: 12,
                exp_year: 2024,
                cvc: '123'
            }
        });

        // Send token.id to server (NOT card details)
        """
        pass

    @staticmethod
    def charge_with_token(token_id, amount):
        """Charge using token (server-side)."""
        # Your server only sees the token, never the card number
        stripe.api_key = "sk_..."

        charge = stripe.Charge.create(
            amount=amount,
            currency="usd",
            source=token_id,  # Token instead of card details
            description="Payment"
        )

        return charge

    @staticmethod
    def store_payment_method(customer_id, payment_method_token):
        """Store payment method as token for future use."""
        stripe.Customer.modify(
            customer_id,
            source=payment_method_token
        )

        # Store only customer_id and payment_method_id in your database
        # NEVER store actual card details
        return {
            'customer_id': customer_id,
            'has_payment_method': True
            # DO NOT store: card number, CVV, etc.
        }
Custom Tokenization (Advanced)
import secrets
from cryptography.fernet import Fernet

class TokenVault:
    """Secure token vault for card data (if you must store it)."""

    def __init__(self, encryption_key):
        self.cipher = Fernet(encryption_key)
        self.vault = {}  # In production: use encrypted database

    def tokenize(self, card_data):
        """Convert card data to token."""
        # Generate secure random token
        token = secrets.token_urlsafe(32)

        # Encrypt card data
        encrypted = self.cipher.encrypt(json.dumps(card_data).encode())

        # Store token -> encrypted data mapping
        self.vault[token] = encrypted

        return token

    def detokenize(self, token):
        """Retrieve card data from token."""
        encrypted = self.vault.get(token)
        if not encrypted:
            raise ValueError("Token not found")

        # Decrypt
        decrypted = self.cipher.decrypt(encrypted)
        return json.loads(decrypted.decode())

    def delete_token(self, token):
        """Remove token from vault."""
        self.vault.pop(token, None)
Encryption
Data at Rest
from cryptography.hazmat.primitives.ciphers.aead import AESGCM
import os

class EncryptedStorage:
    """Encrypt data at rest using AES-256-GCM."""

    def __init__(self, encryption_key):
        """Initialize with 256-bit key."""
        self.key = encryption_key  # Must be 32 bytes

    def encrypt(self, plaintext):
        """Encrypt data."""
        # Generate random nonce
        nonce = os.urandom(12)

        # Encrypt
        aesgcm = AESGCM(self.key)
        ciphertext = aesgcm.encrypt(nonce, plaintext.encode(), None)

        # Return nonce + ciphertext
        return nonce + ciphertext

    def decrypt(self, encrypted_data):
        """Decrypt data."""
        # Extract nonce and ciphertext
        nonce = encrypted_data[:12]
        ciphertext = encrypted_data[12:]

        # Decrypt
        aesgcm = AESGCM(self.key)
        plaintext = aesgcm.decrypt(nonce, ciphertext, None)

        return plaintext.decode()

# Usage
storage = EncryptedStorage(os.urandom(32))
encrypted_pan = storage.encrypt("4242424242424242")
# Store encrypted_pan in database
Data in Transit
# Always use TLS 1.2 or higher
# Flask/Django example
app.config['SESSION_COOKIE_SECURE'] = True  # HTTPS only
app.config['SESSION_COOKIE_HTTPONLY'] = True
app.config['SESSION_COOKIE_SAMESITE'] = 'Strict'

# Enforce HTTPS
from flask_talisman import Talisman
Talisman(app, force_https=True)
Additional patterns and templates
More detailed templates and worked examples live in references/details.md. Read that file for the full pattern library.
| 1 | |
| 2 | name pci-compliance |
| 3 | description Implement PCI DSS compliance requirements for secure handling of payment card data and payment systems. Use when securing payment processing, achieving PCI compliance, or implementing payment card security measures. |
| 4 | |
| 5 | |
| 6 | # PCI Compliance |
| 7 | |
| 8 | Master PCI DSS (Payment Card Industry Data Security Standard) compliance for secure payment processing and handling of cardholder data. |
| 9 | |
| 10 | ## When to Use This Skill |
| 11 | |
| 12 | Building payment processing systems |
| 13 | Handling credit card information |
| 14 | Implementing secure payment flows |
| 15 | Conducting PCI compliance audits |
| 16 | Reducing PCI compliance scope |
| 17 | Implementing tokenization and encryption |
| 18 | Preparing for PCI DSS assessments |
| 19 | |
| 20 | ## PCI DSS Requirements (12 Core Requirements) |
| 21 | |
| 22 | ### Build and Maintain Secure Network |
| 23 | |
| 24 | Install and maintain firewall configuration |
| 25 | Don't use vendor-supplied defaults for passwords |
| 26 | |
| 27 | ### Protect Cardholder Data |
| 28 | |
| 29 | Protect stored cardholder data |
| 30 | Encrypt transmission of cardholder data across public networks |
| 31 | |
| 32 | ### Maintain Vulnerability Management |
| 33 | |
| 34 | Protect systems against malware |
| 35 | Develop and maintain secure systems and applications |
| 36 | |
| 37 | ### Implement Strong Access Control |
| 38 | |
| 39 | Restrict access to cardholder data by business need-to-know |
| 40 | Identify and authenticate access to system components |
| 41 | Restrict physical access to cardholder data |
| 42 | |
| 43 | ### Monitor and Test Networks |
| 44 | |
| 45 | Track and monitor all access to network resources and cardholder data |
| 46 | Regularly test security systems and processes |
| 47 | |
| 48 | ### Maintain Information Security Policy |
| 49 | |
| 50 | Maintain a policy that addresses information security |
| 51 | |
| 52 | ## Compliance Levels |
| 53 | |
| 54 | **Level 1**: > 6 million transactions/year (annual ROC required) |
| 55 | **Level 2**: 1-6 million transactions/year (annual SAQ) |
| 56 | **Level 3**: 20,000-1 million e-commerce transactions/year |
| 57 | **Level 4**: < 20,000 e-commerce or < 1 million total transactions |
| 58 | |
| 59 | ## Data Minimization (Never Store) |
| 60 | |
| 61 | |
| 62 | # NEVER STORE THESE |
| 63 | PROHIBITED_DATA = { |
| 64 | 'full_track_data': 'Magnetic stripe data', |
| 65 | 'cvv': 'Card verification code/value', |
| 66 | 'pin': 'PIN or PIN block' |
| 67 | } |
| 68 | |
| 69 | # CAN STORE (if encrypted) |
| 70 | ALLOWED_DATA = { |
| 71 | 'pan': 'Primary Account Number (card number)', |
| 72 | 'cardholder_name': 'Name on card', |
| 73 | 'expiration_date': 'Card expiration', |
| 74 | 'service_code': 'Service code' |
| 75 | } |
| 76 | |
| 77 | class PaymentData: |
| 78 | """Safe payment data handling.""" |
| 79 | |
| 80 | def __init__(self): |
| 81 | self.prohibited_fields = ['cvv', 'cvv2', 'cvc', 'pin'] |
| 82 | |
| 83 | def sanitize_log(self, data): |
| 84 | """Remove sensitive data from logs.""" |
| 85 | sanitized = data.copy() |
| 86 | |
| 87 | # Mask PAN |
| 88 | if 'card_number' in sanitized: |
| 89 | card = sanitized['card_number'] |
| 90 | sanitized['card_number'] = f"{card[:6]}{'*' * (len(card) - 10)}{card[-4:]}" |
| 91 | |
| 92 | # Remove prohibited data |
| 93 | for field in self.prohibited_fields: |
| 94 | sanitized.pop(field, None) |
| 95 | |
| 96 | return sanitized |
| 97 | |
| 98 | def validate_no_prohibited_storage(self, data): |
| 99 | """Ensure no prohibited data is being stored.""" |
| 100 | for field in self.prohibited_fields: |
| 101 | if field in data: |
| 102 | raise SecurityError(f"Attempting to store prohibited field: {field}") |
| 103 | |
| 104 | |
| 105 | ## Tokenization |
| 106 | |
| 107 | ### Using Payment Processor Tokens |
| 108 | |
| 109 | |
| 110 | import stripe |
| 111 | |
| 112 | class TokenizedPayment: |
| 113 | """Handle payments using tokens (no card data on server).""" |
| 114 | |
| 115 | @staticmethod |
| 116 | def create_payment_method_token(card_details): |
| 117 | """Create token from card details (client-side only).""" |
| 118 | # THIS SHOULD ONLY BE DONE CLIENT-SIDE WITH STRIPE.JS |
| 119 | # NEVER send card details to your server |
| 120 | |
| 121 | """ |
| 122 | // Frontend JavaScript |
| 123 | const stripe = Stripe('pk_...'); |
| 124 | |
| 125 | const {token, error} = await stripe.createToken({ |
| 126 | card: { |
| 127 | number: '4242424242424242', |
| 128 | exp_month: 12, |
| 129 | exp_year: 2024, |
| 130 | cvc: '123' |
| 131 | } |
| 132 | }); |
| 133 | |
| 134 | // Send token.id to server (NOT card details) |
| 135 | """ |
| 136 | pass |
| 137 | |
| 138 | @staticmethod |
| 139 | def charge_with_token(token_id, amount): |
| 140 | """Charge using token (server-side).""" |
| 141 | # Your server only sees the token, never the card number |
| 142 | stripe.api_key = "sk_..." |
| 143 | |
| 144 | charge = stripe.Charge.create( |
| 145 | amount=amount, |
| 146 | currency="usd", |
| 147 | source=token_id, # Token instead of card details |
| 148 | description="Payment" |
| 149 | ) |
| 150 | |
| 151 | return charge |
| 152 | |
| 153 | @staticmethod |
| 154 | def store_payment_method(customer_id, payment_method_token): |
| 155 | """Store payment method as token for future use.""" |
| 156 | stripe.Customer.modify( |
| 157 | customer_id, |
| 158 | source=payment_method_token |
| 159 | ) |
| 160 | |
| 161 | # Store only customer_id and payment_method_id in your database |
| 162 | # NEVER store actual card details |
| 163 | return { |
| 164 | 'customer_id': customer_id, |
| 165 | 'has_payment_method': True |
| 166 | # DO NOT store: card number, CVV, etc. |
| 167 | } |
| 168 | |
| 169 | |
| 170 | ### Custom Tokenization (Advanced) |
| 171 | |
| 172 | |
| 173 | import secrets |
| 174 | from cryptography.fernet import Fernet |
| 175 | |
| 176 | class TokenVault: |
| 177 | """Secure token vault for card data (if you must store it).""" |
| 178 | |
| 179 | def __init__(self, encryption_key): |
| 180 | self.cipher = Fernet(encryption_key) |
| 181 | self.vault = {} # In production: use encrypted database |
| 182 | |
| 183 | def tokenize(self, card_data): |
| 184 | """Convert card data to token.""" |
| 185 | # Generate secure random token |
| 186 | token = secrets.token_urlsafe(32) |
| 187 | |
| 188 | # Encrypt card data |
| 189 | encrypted = self.cipher.encrypt(json.dumps(card_data).encode()) |
| 190 | |
| 191 | # Store token -> encrypted data mapping |
| 192 | self.vault[token] = encrypted |
| 193 | |
| 194 | return token |
| 195 | |
| 196 | def detokenize(self, token): |
| 197 | """Retrieve card data from token.""" |
| 198 | encrypted = self.vault.get(token) |
| 199 | if not encrypted: |
| 200 | raise ValueError("Token not found") |
| 201 | |
| 202 | # Decrypt |
| 203 | decrypted = self.cipher.decrypt(encrypted) |
| 204 | return json.loads(decrypted.decode()) |
| 205 | |
| 206 | def delete_token(self, token): |
| 207 | """Remove token from vault.""" |
| 208 | self.vault.pop(token, None) |
| 209 | |
| 210 | |
| 211 | ## Encryption |
| 212 | |
| 213 | ### Data at Rest |
| 214 | |
| 215 | |
| 216 | from cryptography.hazmat.primitives.ciphers.aead import AESGCM |
| 217 | import os |
| 218 | |
| 219 | class EncryptedStorage: |
| 220 | """Encrypt data at rest using AES-256-GCM.""" |
| 221 | |
| 222 | def __init__(self, encryption_key): |
| 223 | """Initialize with 256-bit key.""" |
| 224 | self.key = encryption_key # Must be 32 bytes |
| 225 | |
| 226 | def encrypt(self, plaintext): |
| 227 | """Encrypt data.""" |
| 228 | # Generate random nonce |
| 229 | nonce = os.urandom(12) |
| 230 | |
| 231 | # Encrypt |
| 232 | aesgcm = AESGCM(self.key) |
| 233 | ciphertext = aesgcm.encrypt(nonce, plaintext.encode(), None) |
| 234 | |
| 235 | # Return nonce + ciphertext |
| 236 | return nonce + ciphertext |
| 237 | |
| 238 | def decrypt(self, encrypted_data): |
| 239 | """Decrypt data.""" |
| 240 | # Extract nonce and ciphertext |
| 241 | nonce = encrypted_data[:12] |
| 242 | ciphertext = encrypted_data[12:] |
| 243 | |
| 244 | # Decrypt |
| 245 | aesgcm = AESGCM(self.key) |
| 246 | plaintext = aesgcm.decrypt(nonce, ciphertext, None) |
| 247 | |
| 248 | return plaintext.decode() |
| 249 | |
| 250 | # Usage |
| 251 | storage = EncryptedStorage(os.urandom(32)) |
| 252 | encrypted_pan = storage.encrypt("4242424242424242") |
| 253 | # Store encrypted_pan in database |
| 254 | |
| 255 | |
| 256 | ### Data in Transit |
| 257 | |
| 258 | |
| 259 | # Always use TLS 1.2 or higher |
| 260 | # Flask/Django example |
| 261 | app.config['SESSION_COOKIE_SECURE'] = True # HTTPS only |
| 262 | app.config['SESSION_COOKIE_HTTPONLY'] = True |
| 263 | app.config['SESSION_COOKIE_SAMESITE'] = 'Strict' |
| 264 | |
| 265 | # Enforce HTTPS |
| 266 | from flask_talisman import Talisman |
| 267 | Talisman(app, force_https=True) |
| 268 | |
| 269 | |
| 270 | ## Additional patterns and templates |
| 271 | |
| 272 | More detailed templates and worked examples live in `references/details.md`. Read that file for the full pattern library. |
| 273 | |
| 274 |
Details
- Updated
- Sep 21, 2026
- License
- MIT
- Stars on the repo
- ★ 39,857
- Checked
- Source
- wshobson/agents ↗
- Creator
- wshobson · 179 listings
Similar skills
See all →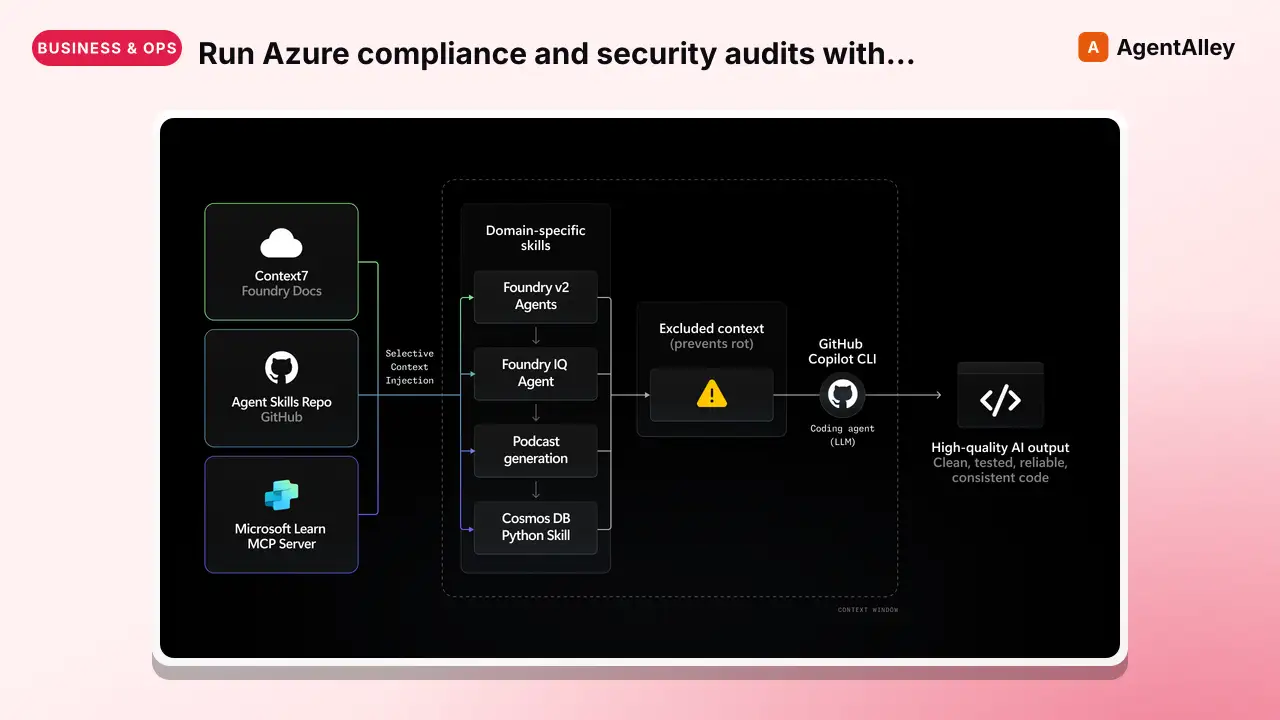 SkillRun Azure compliance and security audits with azqr plus KeyAzure Compliance & Security Auditing
 microsoft/skills · by microsoftRun Azure compliance and security audits with azqr plus Key Vault expiration checks. Covers best-practice assessment, resource review, policy/compliance validation, and security posture checks. WHEN: compliance scan, security audit, BEFORE running azqr (compliance cli tool), Azure best practices, Key Vault expiration check, expired certificates, expiring secrets, orphaned resources, compliance assessment.★ 3.1k GitHub stars
 MCPReviews completed implementation for governing-sourceCode reviewer
 shinpr/claude-code-workflows · by shinprReviews completed implementation for governing-source compliance, scope economy, repository quality policy, and material code correctness. Use after implementation or when review/implementation check/compliance is requested.★ 687 GitHub stars
 SkillImplement GDPR-compliant data handling with consentGdpr data handling
 wshobson/agents · by wshobsonImplement GDPR-compliant data handling with consent management, data subject rights, and privacy by design. Use when building systems that process EU personal data, implementing privacy controls, or conducting GDPR compliance reviews.★ 39.9k GitHub stars
 MCPDraft privacy policies, terms of service, disclaimersLegal advisorwshobson/agents · by wshobsonDraft privacy policies, terms of service, disclaimers, and legal notices. Creates GDPR-compliant texts, cookie policies, and data processing agreements. Use PROACTIVELY for legal documentation, compliance texts, or regulatory requirements.★ 39.9k GitHub stars
 SkillData privacy and regulatory compliance specialist for GDPRData privacy compliance
 davila7/claude-code-templates · by davila7Data privacy and regulatory compliance specialist for GDPR, CCPA, HIPAA, and international data protection laws. Use when implementing privacy controls, conducting data protection impact assessments, ensuring regulatory compliance, or managing data subject rights. Expert in consent management, data minimization, and privacy-by-design principles.★ 32.3k GitHub stars
 SkillSenior FDA consultant and specialist for medical deviceFda consultant specialistdavila7/claude-code-templates · by davila7Senior FDA consultant and specialist for medical device companies including HIPAA compliance and requirement management. Provides FDA pathway expertise, QSR compliance, cybersecurity guidance, and regulatory submission support. Use for FDA submission planning, QSR compliance assessments, HIPAA evaluations, and FDA regulatory strategy development.★ 32.3k GitHub stars
More from wshobson
 SkillMaster C/.NET backend development patterns for buildingwshobson/agents · by wshobsonMaster C#/.NET backend development patterns for building robust APIs, MCP servers, and enterprise applications. Covers async/await, dependency injection, Entity Framework Core, Dapper, configuration, caching, and testing with xUnit. Use when developing .NET backends, reviewing C# code, or designing API architectures.★ 39.9k GitHub stars
 SkillImplement WCAG 2.2 compliant interfaces with mobileAccessibility compliancewshobson/agents · by wshobsonImplement WCAG 2.2 compliant interfaces with mobile accessibility, inclusive design patterns, and assistive technology support. Use when auditing accessibility, implementing ARIA patterns, building for screen readers, or ensuring inclusive user experiences.★ 39.9k GitHub stars
 SkillMaster Material Design 3 and Jetpack Compose patternsAndroid Mobile Designwshobson/agents · by wshobsonMaster Material Design 3 and Jetpack Compose patterns for building native Android apps. Use when designing Android interfaces, implementing Compose UI, or following Google's Material Design guidelines.★ 39.9k GitHub stars
 SkillMigrate from AngularJS to Angular using hybrid modeAngular migrationwshobson/agents · by wshobsonMigrate from AngularJS to Angular using hybrid mode, incremental component rewriting, and dependency injection updates. Use when upgrading AngularJS applications, planning framework migrations, or modernizing legacy Angular code.★ 39.9k GitHub stars
 SkillUnderstand anti-reversing, obfuscationAnti reversing techniqueswshobson/agents · by wshobsonUnderstand anti-reversing, obfuscation, and protection techniques encountered during software analysis. Use this skill when analyzing malware evasion techniques, when implementing anti-debugging protections for CTF challenges, when reverse engineering packed binaries, or when building security research tools that need to detect virtualized environments.★ 39.9k GitHub stars
 SkillBuild production Apache Airflow DAGs with best practicesApache Airflow DAG Patternswshobson/agents · by wshobsonBuild production Apache Airflow DAGs with best practices for operators, sensors, testing, and deployment. Use when creating data pipelines, orchestrating workflows, or scheduling batch jobs.★ 39.9k GitHub stars